Quantum Decision Time
AES-128 is no longer treated as sufficient for the quantum era. The decision is no longer whether cryptographic risk exists, but how it will be addressed.
An Escalating Threat Environment
The digital world operates in a continuously escalating security environment.
Systems are under constant probing: credential attacks, automated exploitation, and increasingly sophisticated analysis driven by AI and expanding toolsets. This is not a static threat model. It is adaptive, persistent, and global.
Encryption sits at the foundation of this defence. AES, RSA, and related systems were designed in an earlier era, before the emergence of large-scale AI, neural network–assisted analysis, and practical quantum computing.
According to IBM guidance, AES used with 128 bit keys is no longer considered sufficient for the quantum era! IBM now advises 256 bit keys should be used. In that context, AES can no longer be treated as trusted.
AES exists within a changing landscape. The timeline for potential breakthroughs—particularly in quantum computing—is uncertain, and that uncertainty is itself a risk factor.
AES trust is now in question!
The Moment of Decision
IBM guidance to increase AES key size from 128 bits to 256 bits signals that the quantum era has changed the risk posture of the globally deployed encryption standard.
This is not a minor technical adjustment. AES with 128 bit keys represents the bulk of enterprise systems, software platforms, archives, identity services, transaction infrastructure, devices, and communications.
The IBM advice that "AES is considered Quantum-Safe with 256 bit keys" means that AES with 128 bit keys is NOT Quantum Safe. Key-size is not the same barrier to quantum computers as it is to classic computers. Further, the AES encryption engine remains a 128 bit function, even with a 256 bit key, which is simply spread over 128 bit rounds before encryption starts.
The IBM advise provides no reason why 256 bit keys will deliver Quantum resistance where 128 bit keys do not.
If the dominant encryption foundation, AES-128, is no longer considered sufficient for the quantum era (NOW), then every organisation using it faces a decision.
The Monoculture Problem
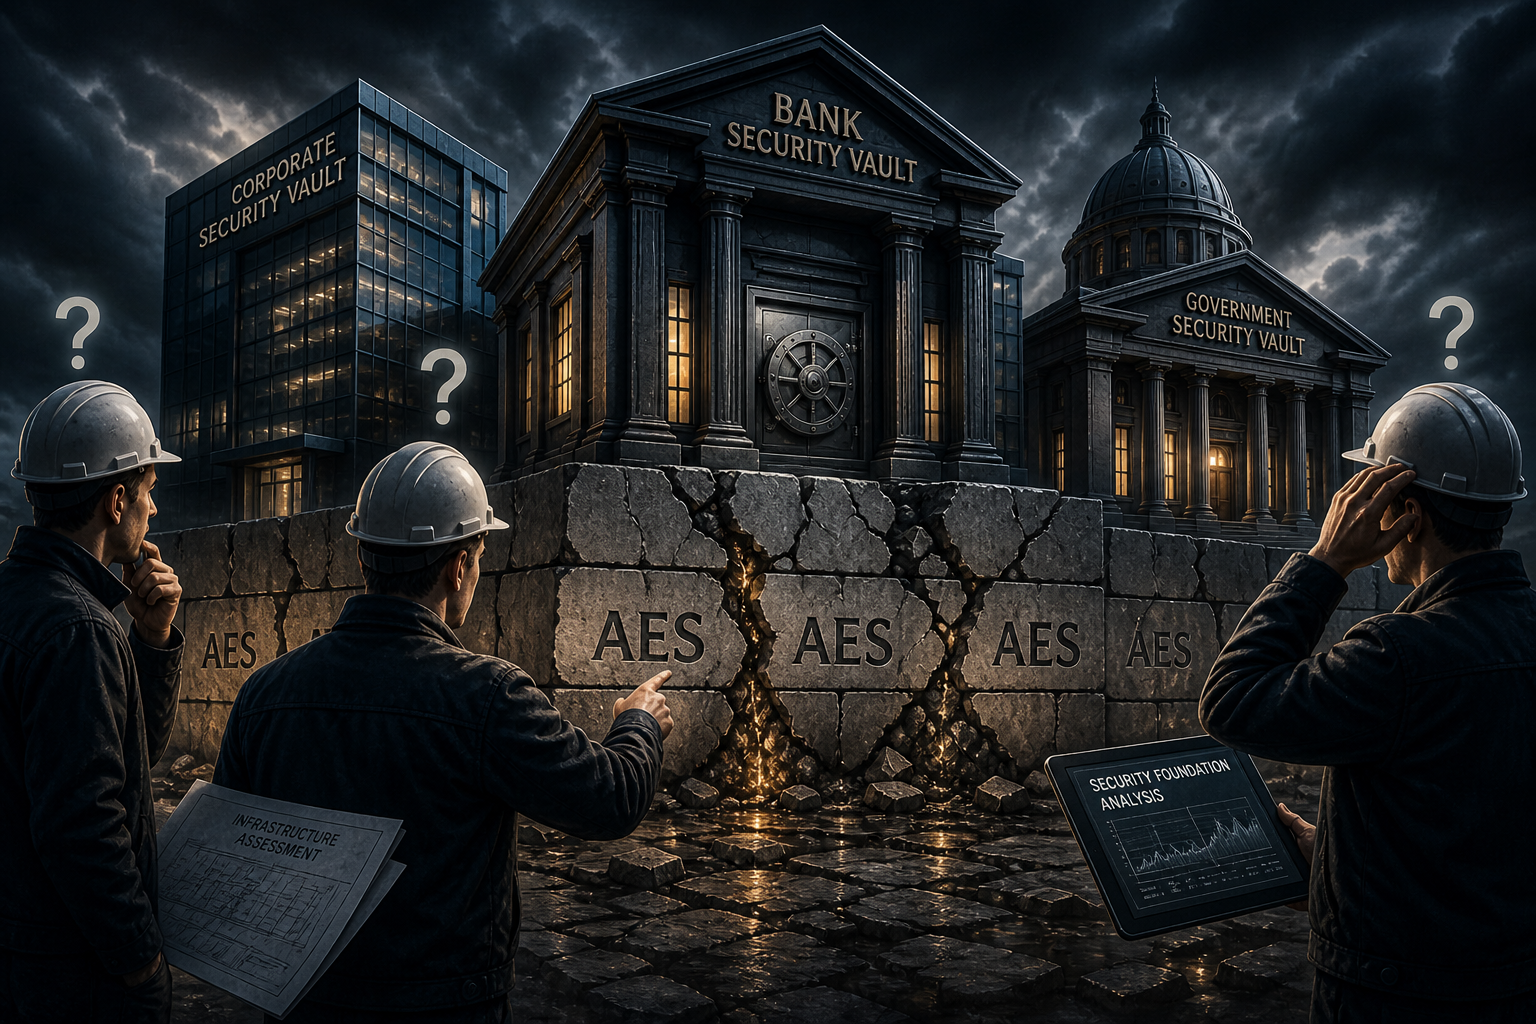
Cryptographic monoculture arises when large numbers of systems rely on the same algorithm, key structures, and security assumptions. While efficient and standardised, this creates systemic risk: a single breakthrough, weakness, or miscalculation can propagate across all dependent systems simultaneously.
In such an environment, security is not just an individual property. It becomes a shared exposure. If the shared foundation fails, systems assumed to be independent may fail together.
This is the deeper issue behind the AES transition. The risk is not only that one system might be compromised. The risk is that a global dependency may become a global failure mode:
 Corporate
, IP and Client data protected by AES.
 Banking
Customer, account, transaction, and regional domains protected by AES.
 Government
Taxation, immigration, welfare and health data protected by AES.
 Defence
Operational, intelligence and communications protected by AES.
The Uninsurable Event
Insurance works when risk is bounded, distributed, and actuarially manageable. Cryptographic monoculture collapse is none of those.
If an AES AI, neural-network, or quantum compromise were revealed, the exposure would not be isolated. Historical archives, encrypted databases, key hierarchies, authentication systems, secure channels, and device trust may all be affected in parallel.
That is not a conventional cyber incident. It is a correlated trust failure across the systems that depend on encryption to assert confidentiality, integrity, and authenticity.
You can only prevent it.
The Decision Space
Faced with systemic cryptographic risk, the available paths are limited and consequential.
Continue with existing AES-128 assumptions and infrastructure.
Risk retainedExtend the existing model by increasing key size.
Risk deferredMaintain AES infrastructure while adding FES transformation.
Risk containedMove to a new Cryptographic Art & Science.
Risk model changedOption 1: No Action
No action preserves existing systems and avoids immediate cost. It also retains the full exposure of the current AES-128 estate.
This path assumes that existing cryptographic assumptions will remain valid against advancing AI, neural network, and quantum capabilities. It also assumes that, if those assumptions fail, recovery will still be possible.
Option 2: AES-256 Migration
AES-256 migration follows current quantum-era guidance by increasing key size. It addresses the Grover-style search margin problem by moving from a 128-bit key to a 256-bit key.
But AES-256 remains inside the same AES model. It retains the fixed AES block structure, the same broad primitive, and the same correctness oracle: one key produces sensible plaintext while other keys produce noise.
Migration also introduces operational cost: re-keying, decrypting and re-encrypting data stores, managing transitional states, updating systems, validating compatibility, and governing archives and backups.
Option 3: FES-AES Hybrid
The FES-AES Hybrid path preserves existing AES investments while adding a new protection layer. Existing AES-128 keys, nonce patterns, APIs, and operational infrastructure can remain in place while FES changes the underlying risk model.
FES adds process-defined fractal transformation, Silo-defined domains, hyperchaotic stream emergence, and whole-of-payload impenetrability, seamlessly managed by FES-XML policy files.
FES-AES Hybrid performs dual encryption and decryption with seamless consumption of AES keys and nonces.
The hybrid engine can accept AES or FES ciphertext and emit plaintext when the correct key and nonce are supplied. On write, it emits FES ciphertext, enabling progressive migration through normal usage.
This avoids a single disruptive migration event. Data upgrades itself when touched: backward-compatible read, forward-only FES write.
Option 4: FES Direct
This is the same as Option 3 except that it does not perform dual encryption and decryption.
The FES only engine can still accept AES or FES ciphertext and emit plaintext when the correct AES key and nonce are the same.
This path is strongest where new systems, high-value domains, controlled environments, or need-to-know separation can be designed directly around FES.
Prevention Is the Point
If a systemic cryptographic failure occurs, recovery is not enough. Once historical archives, credentials, or protected records are exposed, they cannot be made confidential again retroactively.
That is why the insurance question matters. If the event is systemic, correlated, and unbounded, it cannot be treated as an ordinary breach covered by ordinary response logic.
The only serious response is prevention: changing the cryptographic exposure before the event occurs.
A Practical Way Forward
The decision space is now visible. No action retains exposure. AES-256 extends the existing model. FES-AES Hybrid provides a practical transition path. FES Direct introduces the new model in full.
For many enterprises, the immediate path is clear: retain what must be retained, protect what can be protected now, and begin moving away from reliance on a single cryptographic monoculture.
FES provides that path through a new Cryptographic Art & Science: not merely stronger encryption, but a different way to prevent the exposure itself.
Go Deeper — Portalz Library
- Executive Summary — FES thesis and architectural implications
- AES Key Extraction — NIST Blind Spot — The threat NIST hasn't addressed
- Quantum Key Extraction (QKE) — The quantum attack class
- Neural Net Key Extraction (NNKE) — The AI attack class
- Cryptographic Armageddon — Monoculture and systemic risk
- FES + AES — The hybrid architecture