AES Armageddon
The systemic risk created when AES post-quantum security is viewed principally through the Grover lens — while no structured AES replacement program is waiting on the other side of a changed threat model.
The Armageddon Thesis
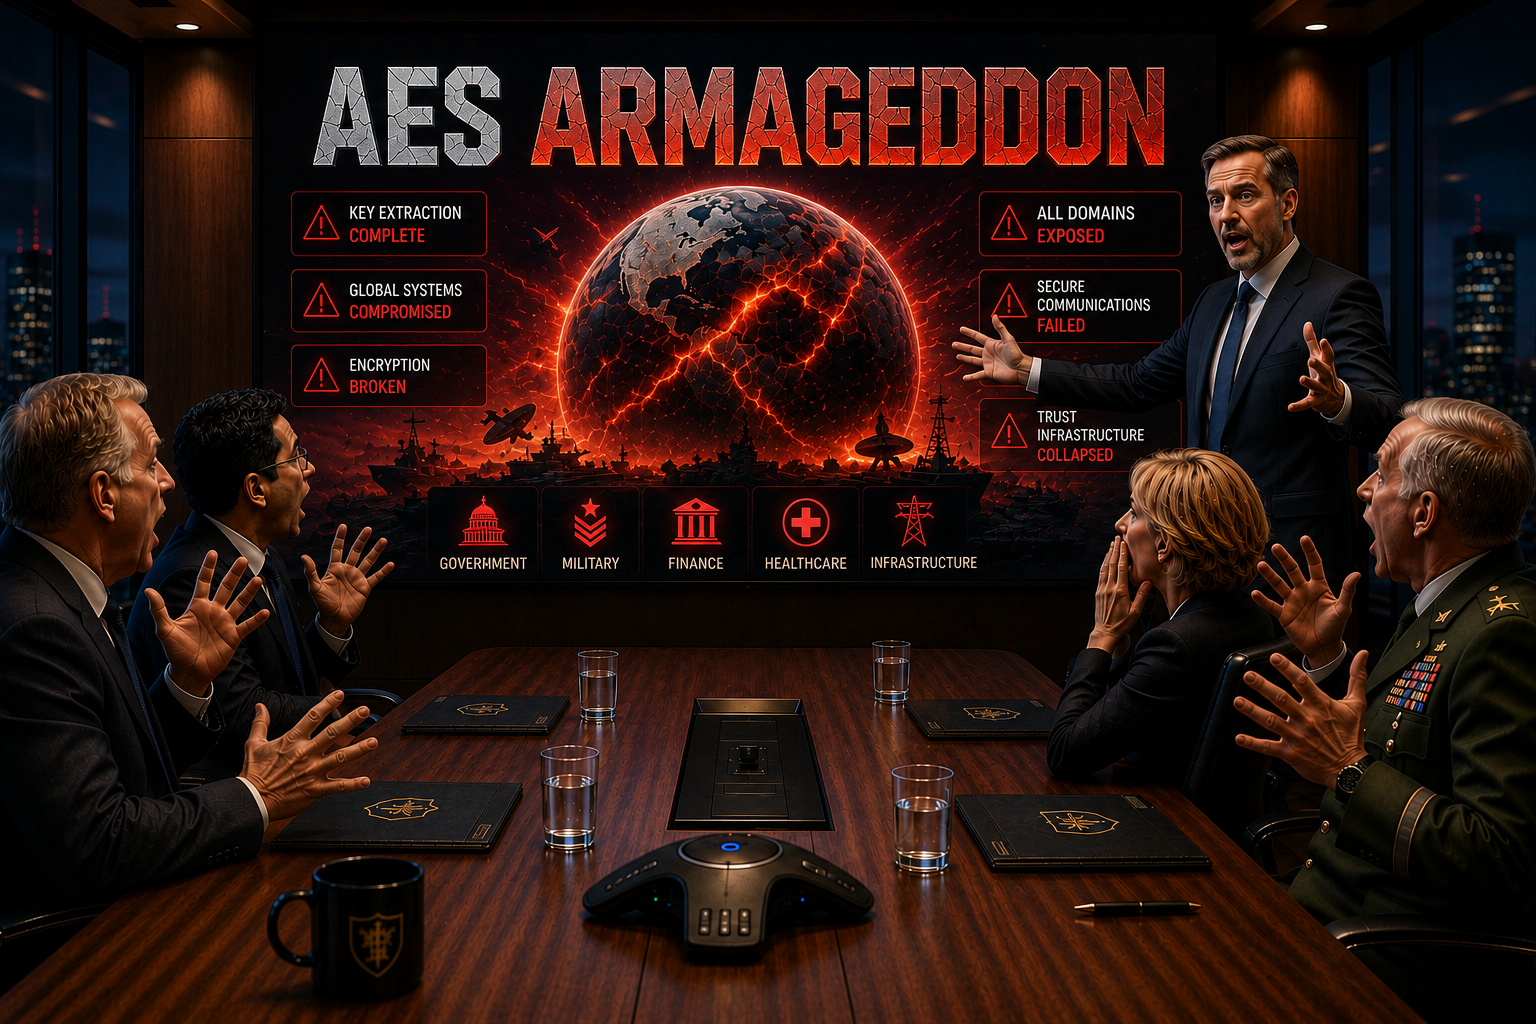
AES Armageddon is not the proposition that AES becomes weaker one day. It is the consequence of the AES quantum threat being recognised only after the world has already run out of preparation time.
It concluded that the threat was far enough away to wait.
That conclusion has been shaped principally by the Grover lens. Grover's algorithm became the dominant model for assessing the quantum threat to symmetric encryption, and its enormous practical resource requirements pushed the perceived AES threat horizon far into the future.
The resulting posture has been one of continued confidence in AES, continued reliance upon increasing key length as the principal quantum mitigation, and no equivalent to the structured public-key Post-Quantum Cryptography replacement program for AES.
Flatow Quantum Key Extraction (QKE) challenges the assumption that Grover defines the earliest possible quantum key-extraction architecture for AES. QKE does not inherit Grover's oscillatory amplitude-amplification process, its enormous iteration count, or the same fault-tolerant quantum-computing requirements.
It may already have disappeared.
That is the Armageddon thesis: not simply that AES may face a quantum threat, but that the world may discover the threat only after years of ciphertext have been created, harvested and retained, while no prepared AES replacement pathway exists.
The Grover Lens
Grover's algorithm approaches the key-space as a search problem. Quantum mechanics accelerates that search, but the architecture remains iterative.
For an AES key-space containing N possible keys, Grover does not directly access the correct key simply because all candidate states can be represented in superposition. Instead, it repeatedly applies an Oracle and diffusion operation, using the quantum properties of phase and interference to progressively amplify the amplitude of the desired state.
→ Amplitude Amplification → Repeat approximately √N times → Read
The quantum speed advantage is therefore substantial, but Grover still performs an oscillatory exploration of the search space across approximately √N sequential iterations. For AES-256, that changes the classical 2256 search problem into an approximately 2128 quantum search problem.
Its quantum advantage does not remove iteration; it dramatically reduces the number of iterations required.
Grover's algorithm emerged in 1996, almost three decades ago, when quantum computers were theoretical and experimental devices rather than today's programmable quantum processors. Its architecture consequently predates practical exploration of the cryptographic implications of assembling large, fully entangled quantum key-spaces.
Grover remains an extraordinarily important quantum algorithm. The AES post-quantum question, however, is whether its iterative search architecture should also define the boundary of what quantum computation can do to an AES key-space.
The Flatow QKE Lens
Flatow Quantum Key Extraction begins from a fundamentally different observation: once the key register has been Hadamard assembled, the complete key-space already exists within the quantum state.
An N-qubit key register does not contain one candidate key waiting to be advanced through a classical iterator. In superposition it represents all 2N possible N-bit key states simultaneously.
QKE takes that fully assembled key-space as the computational starting point. Rather than iteratively exploring candidate keys, the AES Decrypt Unitary operates against the complete key-space in superposition and incorporates the Oracletext pattern-match condition within that computation.
It seeks to exploit the consequence that the complete 2N key-space has already been assembled in superposition.
This produces the fundamental architectural contrast.
↓
Repeated Oracle / diffusion cycles
↓
Oscillatory amplitude amplification
↓
approximately √N iterations
↓
Result
↓
AES Decrypt Unitary
↓
Intrinsic Oracletext pattern match
↓
No key-space iteration
↓
K
How quickly can quantum mechanics search the key-space?
QKE asks:
Why search a key-space that already exists in its entirety?
That distinction is central to AES Armageddon. If Grover is only one possible architecture for exploiting an AES key-space, then Grover's iteration count, logical-qubit requirements and projected hardware timeline cannot by themselves establish the earliest possible AES quantum threat.
By eliminating Grover's iterative search requirement, QKE eclipses the Grover threat model and collapses computational difficulty as the assumed foundation of AES quantum security.
IBM and NIST: Two Different Postures
IBM's current Quantum Safe TLS guidance explicitly says protection for symmetric encryption can be achieved by increasing key sizes, gives the example of moving from AES-128 to AES-256, and advises customers preparing for Quantum Safe TLS to ensure their cipher suite uses AES-256.
NIST's current PQC FAQ takes a less urgent symmetric posture: it states that current applications can continue to use AES-128, AES-192, or AES-256 and that NIST will issue transition guidance for symmetric algorithms when it can foresee a transition need.
Official sources: IBM Quantum Safe TLS · NIST PQC FAQ
AES PQE Apathy
Portalz terms the resulting institutional posture AES PQE Apathy: the absence of urgent AES replacement planning because the quantum threat is treated as distant and manageable within the Grover model.
AES-128 → AES-256 Is Not Trivial
A key-size recommendation looks small on paper. Across deployed digital infrastructure it is a cryptographic transition.
NIST's own crypto-agility work notes that cryptographic transitions are costly, take time, create interoperability issues and disrupt operations. AES-128 to AES-256 may preserve the algorithm name, but that does not make an estate-wide migration trivial.
Official source: NIST — Considerations for Achieving Crypto Agility
The Re-Keying Problem
Migrating the encryption engine does not automatically migrate the ciphertext already protected by AES-128.
Persistent encrypted assets may require new keys, redistribution of key material, changes to key hierarchies, and re-encryption of stored data. Backups, archives, replicas, offline media and long-retention records extend the work far beyond changing a cipher-suite setting.
A Very Expensive Tactical Detour
The AES-256 mitigation is powerful against Grover. But QKE challenges the architecture rather than merely the key-space size.
Under the Flatow QKE ontology, increasing key length enlarges the complete Hadamard-assembled key-space but does not introduce Grover's sequential search burden. If QKE applies equally to AES-256, then a global AES-128 → AES-256 transition may consume enormous time and money without removing the QKE exposure.
a very expensive tactical detour.
The Timeline Discontinuity
The most important difference may not be key length. It may be time.
"How many years until the threat arrives?"
to:
"How many years ago might the capability have arrived?"
This does not assert public evidence that an operational QKE implementation exists. It states the strategic implication of the QKE possibility thesis: the capability may be operational now, and a secret holder would have strong incentives not to disclose it.
Harvest Now, Decrypt Later Makes the Risk Present-Tense
The disclosure date is not the security start date. Long-lived ciphertext can be harvested while the world debates when a sufficiently capable quantum computer will arrive.
If QKE is possible during the confidentiality lifetime of information being encrypted today, then the security requirement manifests today. Migration after acknowledgement protects future data; it cannot recall harvested ciphertext.
QKE Means Key Extraction
QKE is not principally an AES plaintext-decryption proposition. Its output is the key.
The immediate result is one recovered message.
The immediate result is the security credential protecting a cryptographic domain.
One extracted key can have a substantially larger blast radius than one decrypted ciphertext. Its consequence is determined by where that key is used, reused, archived, replicated or retained.
The Output Is a Key Database
Operational key extraction compounds.
A holder of QKE capability would not need to treat every ciphertext as an isolated decryption problem. Extracted keys can be retained as intelligence assets and associated with the systems, identities, endpoints and data domains that use them.
Where Is Plan B for AES?
Public-key cryptography has had years of structured post-quantum replacement work. AES does not have an equivalent mature replacement pathway waiting for a non-Grover AES quantum threat.
there is no migration runway.
The Technical Substance
The strategic case is supported by two deliberately separate technical papers.
AES Is the Headline, Not the Boundary
AES is the focus because of its extraordinary global importance and the systemic consequence of a change to its security assumptions. The underlying architectural concern is broader.
what happens to classical cryptography when computational difficulty is no longer a sufficient security boundary?
The Preparedness Imperative
The defining risk of AES Armageddon is not simply that a new quantum capability may emerge. It is that acknowledgement may arrive after the capability itself.
The QKE-Switch is therefore an information event, not a technology-arrival event. If QKE capability already exists when acknowledgement occurs, the Switch does not mark the beginning of the threat. It reveals that the assumed Grover-based threat horizon was wrong.
At that moment, an AES quantum-threat horizon measured in future years or decades can collapse to the present — and potentially into negative years. The critical question immediately becomes not when QKE will arrive, but how long QKE may already have been operational.
AES remains trusted, deployed and used to create valuable ciphertext while any holder of operational QKE capability has every incentive to preserve that advantage rather than disclose it.
This creates a profound asymmetry. Defenders continue operating according to the accepted Grover timeline, while a QKE-capable adversary could harvest ciphertext, extract keys and accumulate those keys without changing the public perception of AES security.
A defensive alternative must be evaluated, deployable and migrating before the QKE-Switch — not selected after it.
Portalz considers QKE acknowledgement a matter of when, not if. The preparedness question is therefore whether the digital world should continue creating long-lived AES ciphertext while there is no prepared AES Post-Quantum Encryption replacement pathway.
Waiting for public consensus appears conservative only while the threat is assumed to remain in the future. If capability can precede acknowledgement, waiting itself becomes part of the exposure.
It is caused by a global cryptographic monoculture discovering that it prepared for the wrong threat timeline — after that timeline had already been crossed.
Official Reference Points
- IBM Quantum Safe TLS — AES-128 → AES-256 symmetric mitigation and AES-256 preparation guidance.
- IBM Quantum Safe MQ — symmetric key-size treatment under the quantum threat.
- NIST Post-Quantum Cryptography FAQ — current NIST position on AES-128/192/256 and symmetric transition timing.
- NIST Crypto Agility — transition cost, time, interoperability and operational disruption.